
Insights
Product, design, AI, and engineering perspectives from our team.
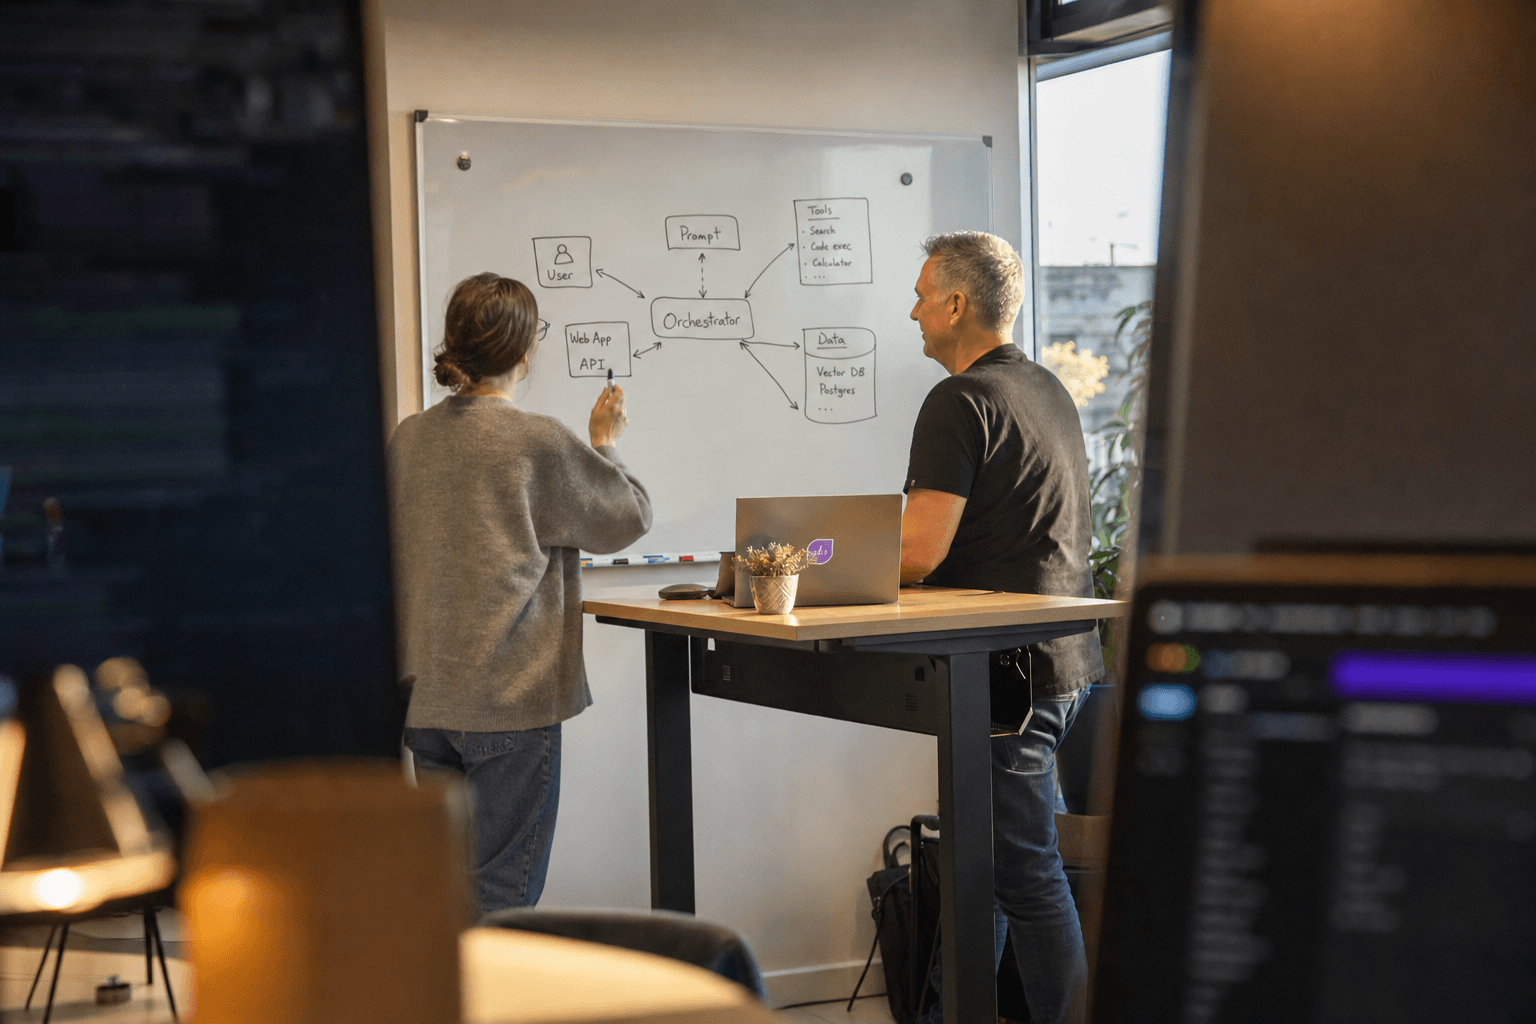
AI Security Review: Threat Modelling LLM Apps Before Launch
A practical, pre-launch framework for threat modelling LLM applications — prompt injection, tool-use data exfiltration, RAG poisoning, and tenant isolation — mapped to OWASP's LLM Top 10 and Australian privacy obligations.
Australia's Voluntary AI Safety Standard: A Compliance Checklist
Australia's Voluntary AI Safety Standard sets out ten guardrails for responsible AI adoption. This practical checklist walks Australian businesses through each guardrail — what it requires, what to do, and how to sequence the work based on your current AI maturity.
The EU AI Act: What Australian Software Exporters Must Do Now
The EU AI Act applies to Australian software and AI vendors selling into Europe, regardless of where they are headquartered. This post explains how the risk tiers work, what high-risk obligations actually require, and a practical compliance path for Australian exporters.
AI in Australian Financial Services: Risk and Compliance
AI offers Australian financial services firms real capability in fraud detection, compliance automation, and customer operations — but only when deployed with a clear view of APRA, ASIC, and Privacy Act obligations. This article covers the primary use cases, the regulatory landscape, and the technical foundations required to get AI into production in a regulated environment.
AI and Intellectual Property: Who Owns What When AI Generates Content?
AI-generated content creates complex ownership questions that traditional Australian IP law wasn't designed to handle. Understanding these challenges is critical for protecting investments and avoiding disputes.
SOC 2 Compliance for AI-Powered Applications: A Technical Guide
SOC 2 compliance for AI applications requires addressing traditional security controls alongside AI-specific risks like model governance and training data handling. This technical guide covers the key implementation strategies for building compliant AI systems.
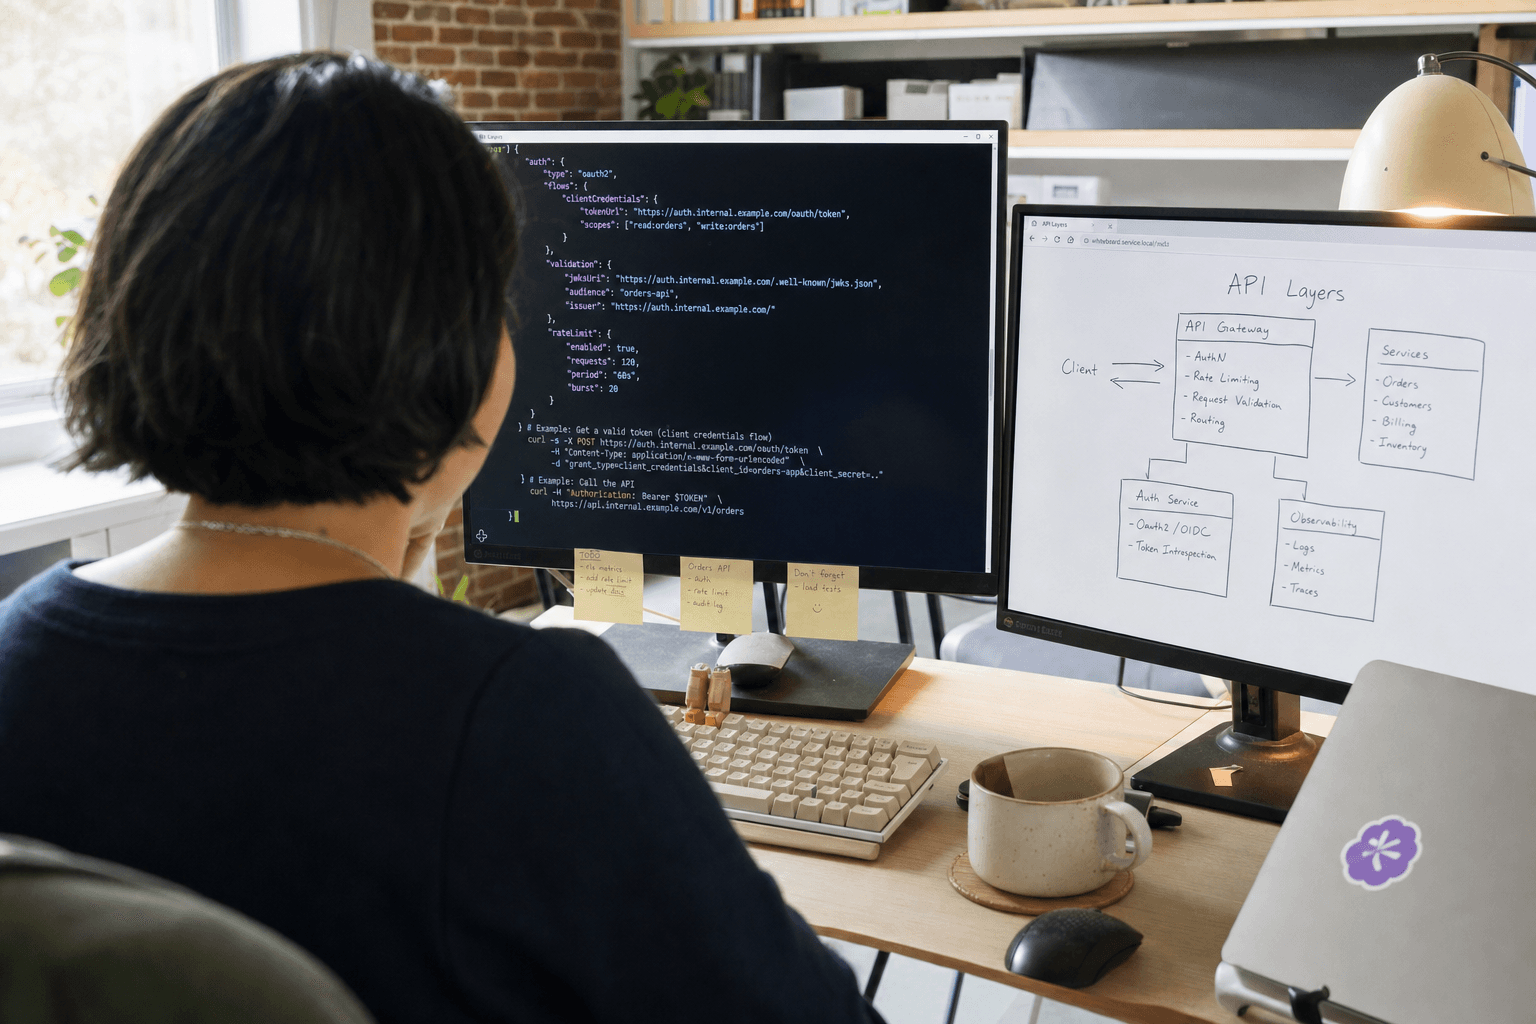
Securing API Endpoints for AI Applications: OWASP Best Practices
AI APIs require layered security addressing traditional vulnerabilities and AI-specific threats like prompt injection and model extraction. Learn OWASP best practices for protecting endpoints from data breaches and service disruption.
Data Privacy and AI in Australia: Navigating the Privacy Act
The Australian Privacy Act applies to AI systems that handle personal information, creating specific obligations around data collection, consent, and cross-border transfers. Understanding these requirements becomes critical as organisations deploy AI capabilities and navigate upcoming privacy reforms.
AI Security: Protecting Your Models, Data, and Users
Production AI systems face unique security challenges from prompt injection to model theft. Learn how to protect your AI models, data, and users with practical security measures designed for Australian organisations.