
Insights
Product, design, AI, and engineering perspectives from our team.
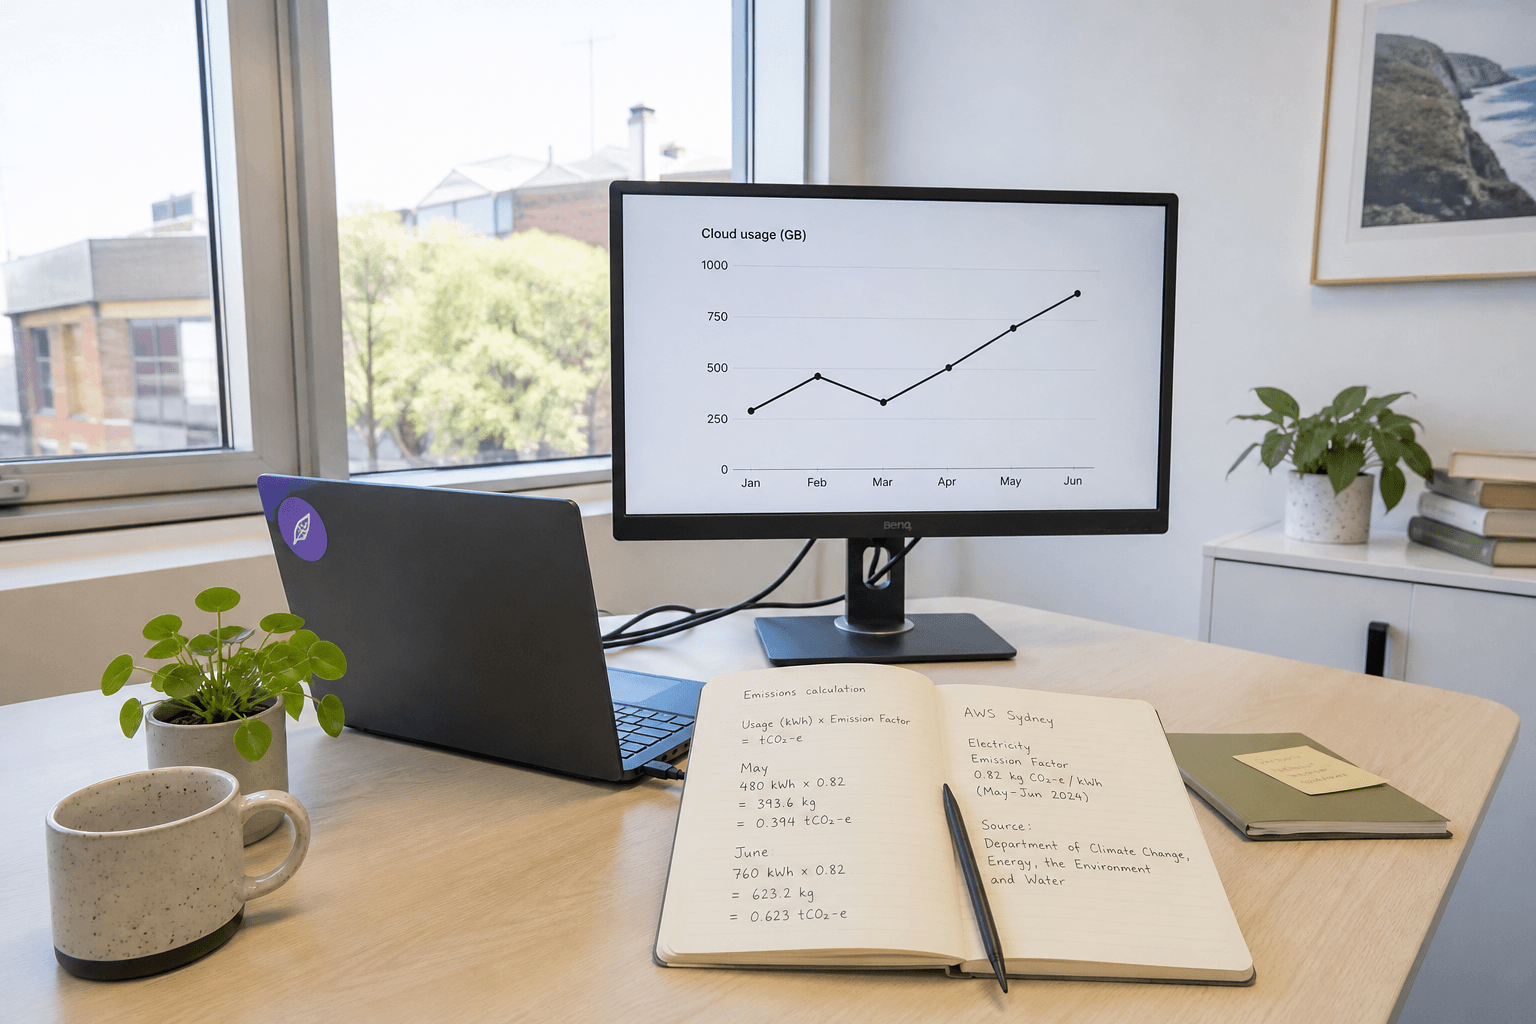
AASB S2 Climate Disclosure: A Guide for Tech & Cloud Teams
AASB S2 brings mandatory climate disclosure to Australian companies — and cloud infrastructure teams are increasingly part of the data trail. Here's what engineering and platform leaders need to know about Scope 1-3 emissions and cloud carbon reporting.
ISO 27001 Certification While Modernising Legacy Systems
A practical look at how Australian fintech, healthtech and insurtech companies can approach ISO 27001 certification alongside legacy infrastructure modernisation — including how it differs from SOC 2 and where the two workstreams overlap.
CPS 230 and AI Vendor Dependency Mapping for Financial Services
APRA's CPS 230 standard, effective from July 2025, requires regulated entities to map dependencies on critical operations — and AI vendors are increasingly part of that picture. Here's how financial services firms can approach AI vendor and model dependency mapping as part of operational resilience planning.
ISO/IEC 42001 Certification: A Guide for Australian Firms
ISO/IEC 42001 is the first certifiable international standard for AI management systems. This guide explains what it requires, how it compares to Australia's Voluntary AI Safety Standard and the EU AI Act, and what to have in place before pursuing certification.
Shadow AI Usage Policies: A Guide for Tech Leaders
Unsanctioned AI tools are already inside your engineering and product teams, whether or not anyone has approved them. Here's how technology and business leaders can identify shadow AI use and build governance that reduces risk without killing productivity.
Cyber Insurance for AI Products: What's Covered, What's Not
Cyber policies generally cover AI-related security incidents but often exclude model performance failures like hallucinations or biased outputs. Here's how CTOs and business leaders should map that gap with their broker.
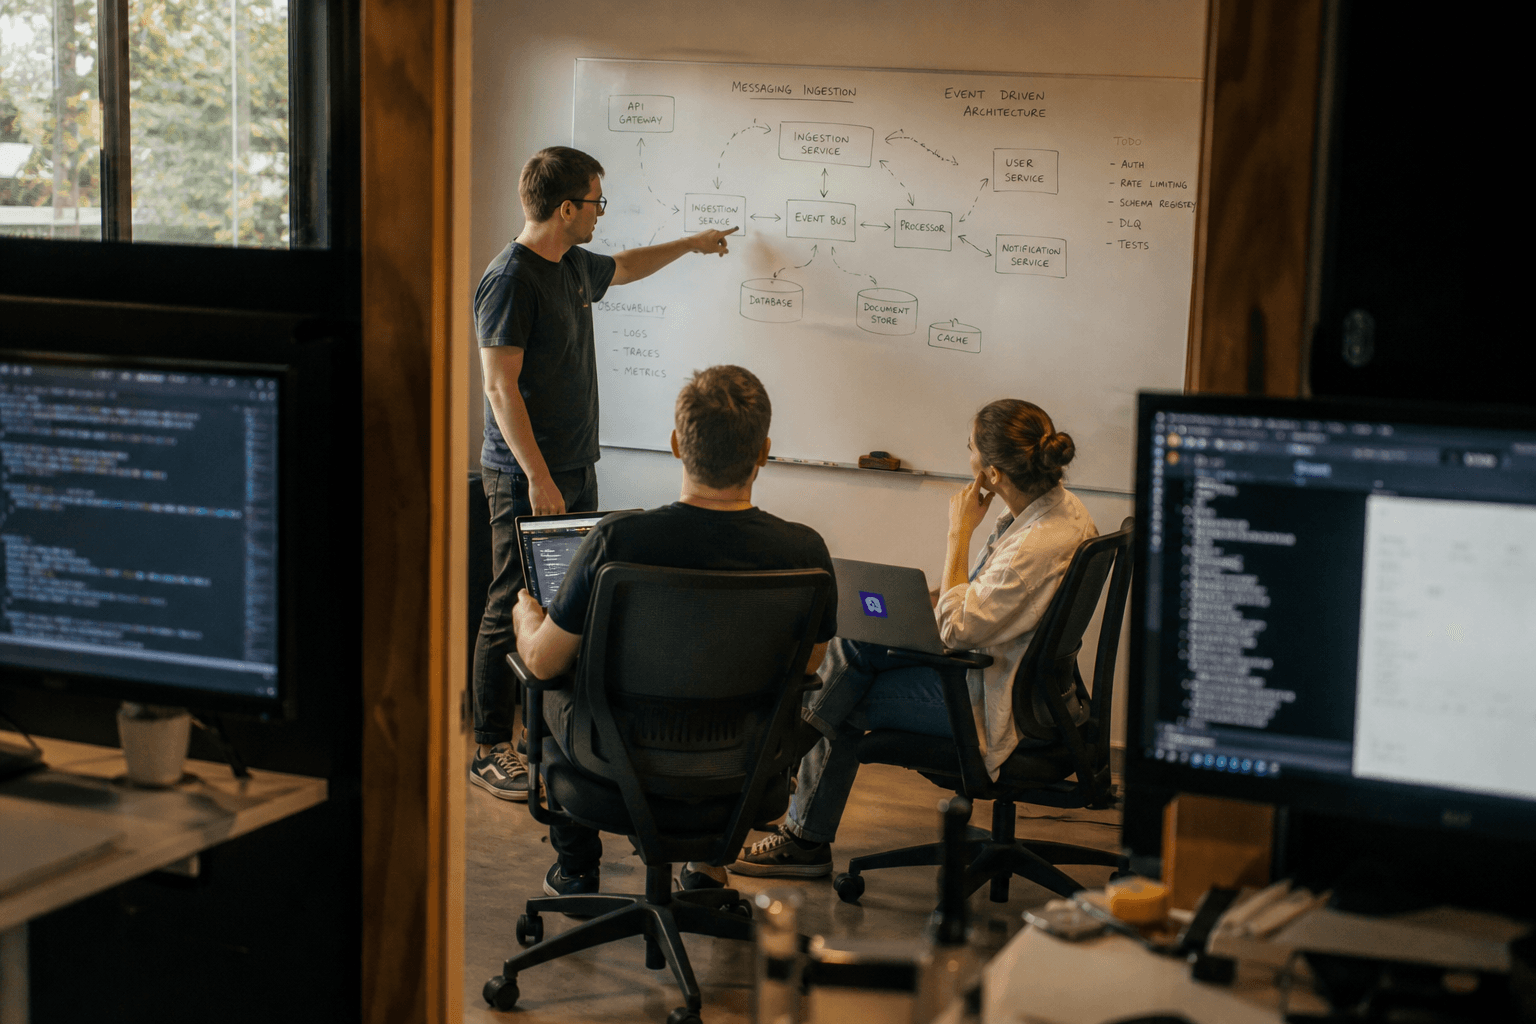
Business Continuity Planning for AI-Dependent Products
Business continuity planning for AI-dependent products means designing systems and processes so AI features keep working, in degraded form if needed, when a model provider has an outage, changes rate limits, or deprecates an API. Here's how to classify critical-path features and design failover accordingly.
AI Services & Data Sovereignty for Regulated Australian Industries
A practical guide for fintech, healthtech, and insurance leaders on where AI training and inference data can legally live under the Privacy Act 1988 and APRA CPS 234 — plus architecture patterns for keeping sensitive data onshore while using cloud AI services.
AI Governance Framework for Australian Mid-Market Companies
Most AI governance frameworks assume an enterprise compliance team the mid-market doesn't have. Here's a right-sized approach — a lean policy set, model inventory, human-in-the-loop rules and vendor due diligence — mapped to Privacy Act reform and the Voluntary AI Safety Standard.