AI Agent Marketplaces: Build vs Integrate Decision Guide
Integrate a marketplace agent when the task is standardised and your data already lives with the vendor. Build custom when the agent is core to your product. Here's the framework, plus how security review should shape the call.
Build vs integrate: the short answer
Integrate a marketplace agent when the task is standardised, your data already sits inside the vendor's ecosystem, and the platform's governance controls meet your compliance posture. Build a custom agent when it needs to reason over proprietary data models, enforce bespoke access controls, or operate across systems the marketplace platform doesn't natively support — and when the capability is a durable, differentiating part of your product rather than a commodity workflow.
That's the framework. The rest of this guide walks through why the decision matters now, what each path actually costs you, and how security review should shape the call before you commit to either one.
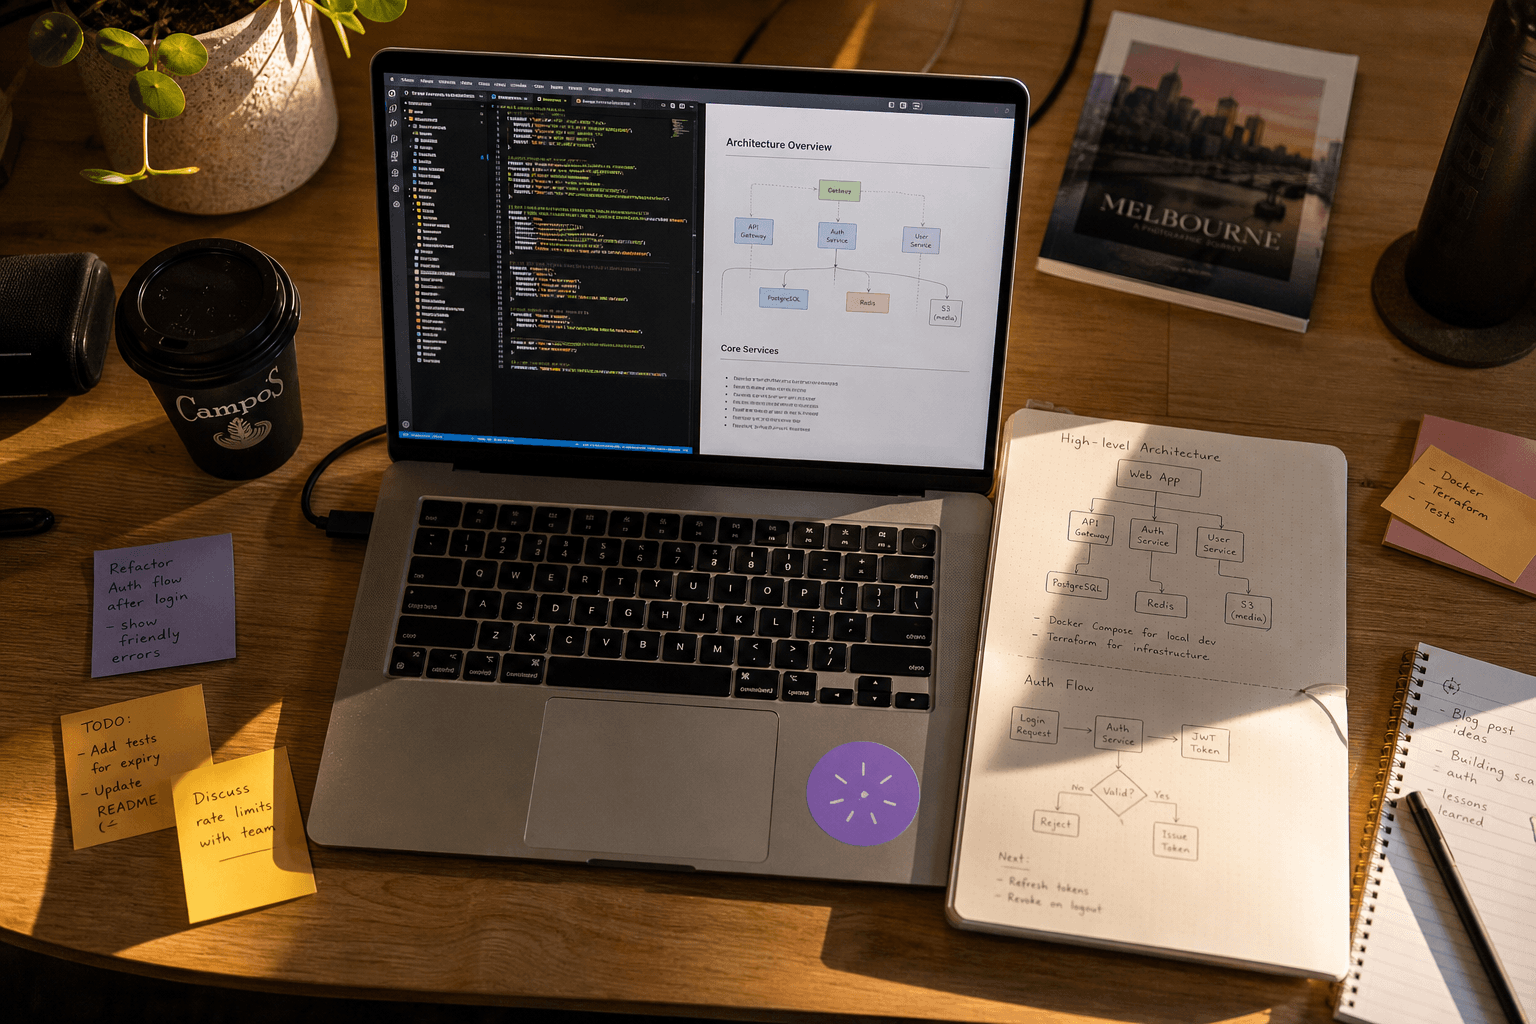
What is an AI agent marketplace?
An AI agent marketplace is a platform where pre-built, third-party AI agents — for tasks like customer support, document processing, or workflow automation — can be discovered, configured, and deployed into an organisation's systems, typically through a managed runtime provided by a cloud vendor. Rather than writing agent orchestration, session handling, and retrieval logic from scratch, a team consumes these as services and focuses engineering effort on the business logic layered on top.
The clearest example of this model in production today is Google's Vertex AI, documented as the Gemini Enterprise Agent Platform. It exposes a managed agent runtime (Reasoning Engines) supporting query, streaming, async, and bidirectional invocation, paired with managed Sessions for stateful interactions, native retrieval-augmented generation, vector search, feature stores, model tuning, and a dedicated governance policy engine — all accessible through SDKs across multiple languages. For organisations already operating on Google Cloud, this is a mature, integrate-first option.
Why does the build vs integrate question matter now?
Technical leaders are under pressure to ship AI capability quickly, and marketplace platforms promise to compress months of orchestration and infrastructure work into a configuration exercise. The question is not whether integration is faster on day one — it almost always is — but whether it remains the right fit once you account for data boundaries, vendor dependency, and the total cost of running the agent over its lifetime.
This is a variant of a decision pattern technical leaders already know well: platform (SaaS) versus bespoke build. Standardised, well-understood problems suit a managed platform — predictable cost, faster time-to-value, but limited ability to adapt to non-standard requirements. Complex, novel, or cross-functional problems — wiring a third-party agent into legacy data infrastructure, internal governance rules, or systems the platform was never designed to touch — tend to need tailored engineering rather than an opinionated vendor workflow. Working through this trade-off properly is part of what our ai product strategy work covers before any code gets written.
When does integrating a marketplace agent make sense?
Integration makes sense when the task is standardised, your data already sits inside the vendor's ecosystem, and the governance controls the platform ships with are sufficient for your compliance posture. If your organisation is already running on Google Cloud with existing IAM, VPC, and data residency controls configured, consuming Vertex AI's Reasoning Engines and Sessions can meaningfully reduce engineering effort on orchestration, retrieval, and state management.
The trade-off is dependency. You inherit the vendor's API surface, release cadence, and pricing model. If the platform's semantic governance engine doesn't express a policy your industry requires — say, a specific data retention rule under the Privacy Act 1988 (Cth) or an APRA CPS 234 control for a regulated financial services workload — you are constrained by what the platform exposes, not what your risk team actually needs.
When does building a custom agent make the stronger case?
Building custom makes sense when the agent needs to reason over proprietary data models, enforce bespoke access controls, or operate across systems the marketplace platform doesn't natively support — legacy mainframes, industry-specific data formats, or a patchwork of acquired systems common in growing technology stacks. A custom build also removes the long-term dependency on a single vendor's roadmap for a capability that is core to your product, not incidental to it.
The cost is upfront engineering effort: your team, or an embedded partner, has to build orchestration, session state, retrieval, and monitoring that a marketplace platform would otherwise provide. This is the right trade when the agent is a durable, differentiating part of your product rather than a commodity workflow. Our ai engineering practice typically starts here — mapping which agent capabilities are genuinely strategic versus which are better consumed as a managed service, and building the parts that need to be yours to own. Where the agent needs to sit alongside an existing monolith or legacy backend, this decision often runs in parallel with broader application modernisation work, since the two constraints — what the platform can reach and what your architecture can expose — tend to be linked.
How should security review and data access boundaries shape the decision?
Security review should happen before the build-vs-integrate decision is finalised, not after a vendor is selected. Every third-party agent — marketplace-sourced or custom — needs a clear answer to what data it can read, what it can write, what external calls it can make, and what happens when it fails or attempts a tool call it shouldn't make.
For marketplace agents, this means auditing the platform's IAM model, understanding what data leaves your environment (even transiently, for inference), and confirming whether the vendor's governance policy engine can actually enforce your access boundaries or merely log violations after the fact. For custom-built agents, the same questions apply but the controls are yours to design and yours to maintain — which is more effort, but gives your security and compliance teams full visibility rather than trusting a vendor's attestation.
Organisations handling health, financial, or other sensitive data should map this against guidance from the Office of the Australian Information Commissioner and relevant sector regulators before any agent — marketplace or custom — is given access to production data. Neither path is inherently safer; both require the same rigour, just applied in different places.
If you're weighing this decision for a specific workload, it's rarely a clean either/or — most organisations end up running some agents on a managed platform and building others in-house, depending on how core each one is to the product. For more on how we think through these trade-offs, see our more insights on AI adoption and legacy modernisation, or get in touch to talk through where your agent sits on that spectrum.
Chris Kerr
Partner at Horizon Labs, an AI product consultancy and venture studio. A commercially focused product and technology leader with 20+ years building and scaling digital platforms, teams, and businesses across SaaS, travel, eCommerce, logistics and transport, and digital marketing — operating at the intersection of product, engineering, and data. Writes about platform strategy, AI transformation, modern data ecosystems, and the operational discipline that separates AI demos from AI products.