Reducing SaaS and Vendor Sprawl as You Scale
As Australian scale-ups grow, SaaS tools and vendor contracts accumulate faster than governance can keep up. This guide covers how to audit, evaluate overlap, negotiate renewals, and cut integration and security overhead.
What Is SaaS Sprawl and Why Does It Happen?
SaaS sprawl is the accumulation of software subscriptions and vendor contracts that occurs when teams independently adopt tools to solve immediate problems, without central visibility or governance. It happens fastest during periods of rapid scaling, when engineering, sales, marketing, and operations teams all buy tools in parallel to keep up with growth, and nobody owns the full picture.
For Australian scale-ups, this usually starts innocently. A team trials a project management tool during a sprint crunch. Another spins up a new observability platform because the existing one does not fit their microservice. A business unit signs a data enrichment tool without looping in engineering. Two years later, the finance team is reconciling dozens of recurring charges, and nobody can say with confidence which tools are still load-bearing.
Why Does Vendor Sprawl Accelerate During Growth?
Vendor sprawl accelerates during growth because decision-making decentralises faster than governance does. As headcount grows, more people have purchasing authority, procurement processes lag behind the pace of hiring, and the cost of any single subscription looks small relative to overall spend — until the sum of all of them becomes material.
Common triggers we see across growing Australian businesses include new team leads bringing over tools from previous employers, product teams adopting point solutions to hit a deadline, and multiple teams solving the same problem (analytics, alerting, feature flagging) independently because there is no shared platform decision. Left unmanaged, this compounds technical debt in the same way an unmanaged monolith does — see our take on application modernisation for how architectural sprawl and vendor sprawl often mirror each other.
How Do You Audit Your Current SaaS and Vendor Portfolio?
A proper audit starts with a complete inventory, not a partial one. Pull every recurring charge from finance systems, corporate cards, and SSO logs — the gap between what finance sees and what your identity provider sees is usually where the surprises live. Cross-reference against your single sign-on or identity provider, since anything not behind SSO is a governance and security risk by definition.
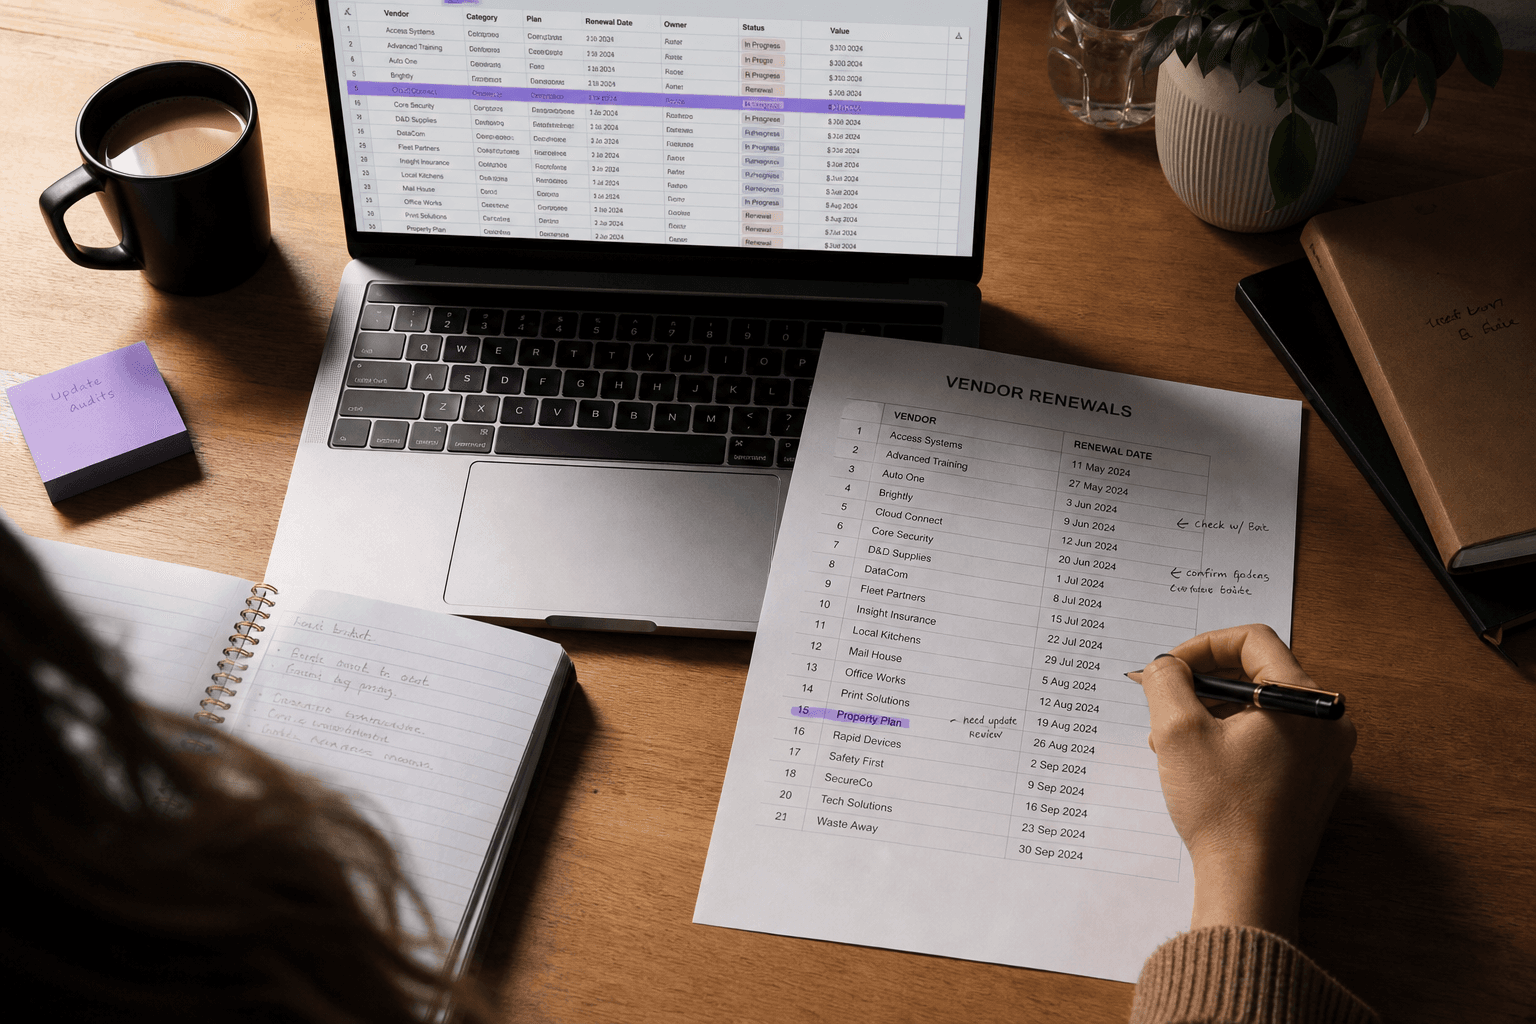
For each tool, capture: owning team, primary use case, number of active users (not licensed seats), contract renewal date, and whether it holds sensitive data. This last point matters for compliance — the Australian Cyber Security Centre's Essential Eight guidance on application control and restricting administrative privileges is a useful lens for flagging which tools warrant closer security review, particularly anything with broad data access or admin-level integrations.
How Do You Evaluate Overlap Between Tools?
Overlap evaluation means mapping tools against the job they do, not their marketing category, because two products in different categories can still solve the same underlying problem. Group tools by function — data visualisation, alerting, task tracking, customer messaging — rather than by vendor name, and look for teams solving the same problem with different products.
When genuine overlap is found, the deciding factors should be: which tool has the deepest adoption, which integrates most cleanly with your core stack, and which has the lower total cost of ownership once you include integration maintenance, not just licence fees. A tool with a cheaper subscription but three custom integrations to maintain is often more expensive than a slightly pricier tool with a native connector.
How Should You Approach Vendor Renewal Negotiations?
Renewal negotiations go better when you walk in with usage data, not just a renewal notice. Vendors expect usage-based conversations at scale-up size, and most have room to move on price, seat count, or contract term when you can show declining or plateaued active usage.
A few practical habits help here: calendar renewal dates 90 days out so you are never negotiating under time pressure, consolidate multi-year contracts where usage is proven and stable, and ask for usage reporting as a standard contract term so the next audit is easier than this one. Where a vendor relationship underpins core infrastructure rather than a point solution, it is worth treating the renewal as a genuine architecture decision, not a procurement formality.
What Integration and Security Overhead Does Sprawl Create?
Each additional SaaS tool adds integration surface area, and integration surface area is where operational and security risk actually lives. Every API connection, webhook, and data sync is a potential failure point and a potential access path that needs monitoring, credential rotation, and ownership.
The less visible cost is engineering time: teams spend meaningful cycles maintaining brittle integrations between overlapping tools instead of building product. Consolidating around a smaller set of well-integrated platforms, backed by solid data infrastructure, reduces both the security surface and the maintenance tax on your engineering team.
Sprawl vs. Consolidated: A Practical Comparison
| Dimension | Sprawled state | Consolidated state |
|---|---|---|
| Vendor visibility | Owned by multiple teams, no central register | Central register with owner, cost, and renewal date per tool |
| Security review | Ad hoc, reactive to incidents | Scheduled, tied to data sensitivity and access level |
| Integration maintenance | High — many point-to-point connections | Lower — fewer, well-owned integrations |
| Renewal negotiation | Reactive, near deadline | Proactive, backed by usage data |
| Engineering time cost | Ongoing tax on maintenance | Freed up for product work |
How Do You Prevent Sprawl From Returning?
Preventing sprawl requires a lightweight approval process, not a heavyweight one, because heavy processes get bypassed under deadline pressure. A simple rule — any new recurring SaaS spend above a defined threshold needs sign-off from engineering leadership and a quick security check — catches most sprawl before it compounds.
This is also where a fractional or advisory technology leader earns their keep: someone with the mandate to say no to redundant tools, and the technical credibility for teams to trust the call. Our CTO advisory work often starts exactly here — before any AI or platform initiative, we help leadership teams get a clear, current picture of what they are actually running and paying for.
Where to Start
If you are carrying more SaaS tools and vendor contracts than anyone can name off the top of their head, that is itself the signal to act. Start with the inventory, be honest about usage versus licensed seats, and treat every renewal as a decision point rather than a formality. For more on building the technical foundations that make consolidation stick, browse our insights.
If you're exploring how to bring your vendor and SaaS footprint back under control, we can help — starting with an honest audit of what you are running and what it is actually costing you.
Chris Kerr
Partner at Horizon Labs, an AI product consultancy and venture studio. A commercially focused product and technology leader with 20+ years building and scaling digital platforms, teams, and businesses across SaaS, travel, eCommerce, logistics and transport, and digital marketing — operating at the intersection of product, engineering, and data. Writes about platform strategy, AI transformation, modern data ecosystems, and the operational discipline that separates AI demos from AI products.