Consumer Data Right: Architecting Open Banking APIs
Architecting for Australia's Consumer Data Right comes down to three decisions: accreditation pathway, standards-compliant API design, and consent as an auditable, revocable system of record. Here's how fintech engineering teams should sequence them.
Architecting for Australia's Consumer Data Right (CDR) comes down to three engineering decisions, and they need to be made before a line of integration code is written. First, where your fintech sits in the Data Holder / Accredited Data Recipient model — and which accreditation pathway follows from that. Second, how your API and security layer implements the Consumer Data Standards' technical profile, so you're speaking the regulated dialect rather than an ad hoc one. Third, how you build consent management as a time-bound, revocable, auditable system of record, not a checkbox stored next to a user profile. Get these three right early and the rest of the integration follows a predictable path. Get them wrong, and you're rebuilding core parts of your integration layer post-launch, under audit pressure, while competitors move faster on the same data pipes. The rest of this guide works through each decision in the order engineering teams typically need to resolve them.
What Is the Consumer Data Right, and Why Does It Matter for Fintech Engineering Teams?
The Consumer Data Right is Australian legislation, administered by the Australian Competition and Consumer Commission (ACCC) under the Competition and Consumer Act 2010, that gives consumers the right to direct that their data — starting with banking, and extended to energy and telecommunications — be shared securely with accredited third parties. For fintech engineering teams, it matters because it defines who you can exchange data with, under what technical standard, and with what consent evidence you must be able to produce on demand.
A useful working definition: the CDR is a regulated data-sharing framework that separates Data Holders (typically banks, who hold the consumer's data) from Accredited Data Recipients (organisations, potentially including your fintech, that receive data with consumer consent). The Data Standards Body, working alongside the ACCC and the Office of the Australian Information Commissioner (OAIC), publishes the technical and consumer-experience standards both sides must implement.
How Does Accreditation Work Under the CDR?
Accreditation is the gate that determines whether your fintech can receive CDR data directly, or must rely on an intermediary. The ACCC maintains a Register of Accredited Persons, and accreditation comes in tiers with different obligation levels — the tier you pursue should be an early architecture decision, not an afterthought bolted on before launch.
| Accreditation pathway | What it means for engineering | Typical fit |
|---|---|---|
| Unrestricted accreditation | Full obligations: security, consent, and data-handling standards implemented and audited end-to-end | Fintechs building CDR data use as a core, long-term product capability |
| Sponsored / affiliate accreditation | An accredited sponsor carries some compliance burden; your team still integrates to the data standard | Teams wanting to move faster while sharing accountability with a sponsor |
| Representative arrangements | You operate under an existing accredited entity's accreditation, with a narrower scope of direct obligation | Early-stage products testing CDR-dependent features before committing to full accreditation |
The right pathway depends on your product roadmap, risk appetite, and how central open banking data is to your core proposition. This is exactly the kind of build-versus-partner decision worth working through with technical leadership, and it overlaps closely with the questions we work through in ai product strategy engagements — because CDR data is frequently the input layer for AI-driven credit, cash-flow, or personalisation features, and the accreditation pathway you choose constrains what those features can do later.
What Are the Consumer Data Standards, and How Do They Shape API Architecture?
The Consumer Data Standards define the technical shape of every CDR interaction — the API structures, authentication flows, and security profile that both Data Holders and Recipients must implement consistently. Architecturally, this means your integration layer needs to speak a regulated dialect, not an ad hoc one your team invents.
In practice, this pushes fintech engineering teams toward a security profile built on OAuth 2.0 and OpenID Connect patterns aligned to the Financial-grade API (FAPI) specification, with mutual TLS for holder-to-recipient calls. The standards also cover non-functional expectations — availability, performance, and error handling — that data holders are measured against, which means your integration needs resilience patterns (retries, circuit breakers, graceful degradation) for when a bank's CDR endpoint is slow or unavailable, rather than assuming five-nines availability from every counterparty.
Teams modernising a legacy core banking or lending platform to expose or consume CDR data often find the constraint isn't the CDR API itself, but the brittleness of what sits behind it. That's frequently where application modernisation work — decomposing a monolith so a clean, standards-compliant API layer can sit in front of it — becomes the real unlock. Once that layer exists, it also becomes the natural place to plug in the model-serving and pipeline work covered under ai engineering, since CDR-sourced data typically needs to reach a feature store or scoring service, not just a screen.
How Should Fintech Teams Architect Consent Management for CDR?
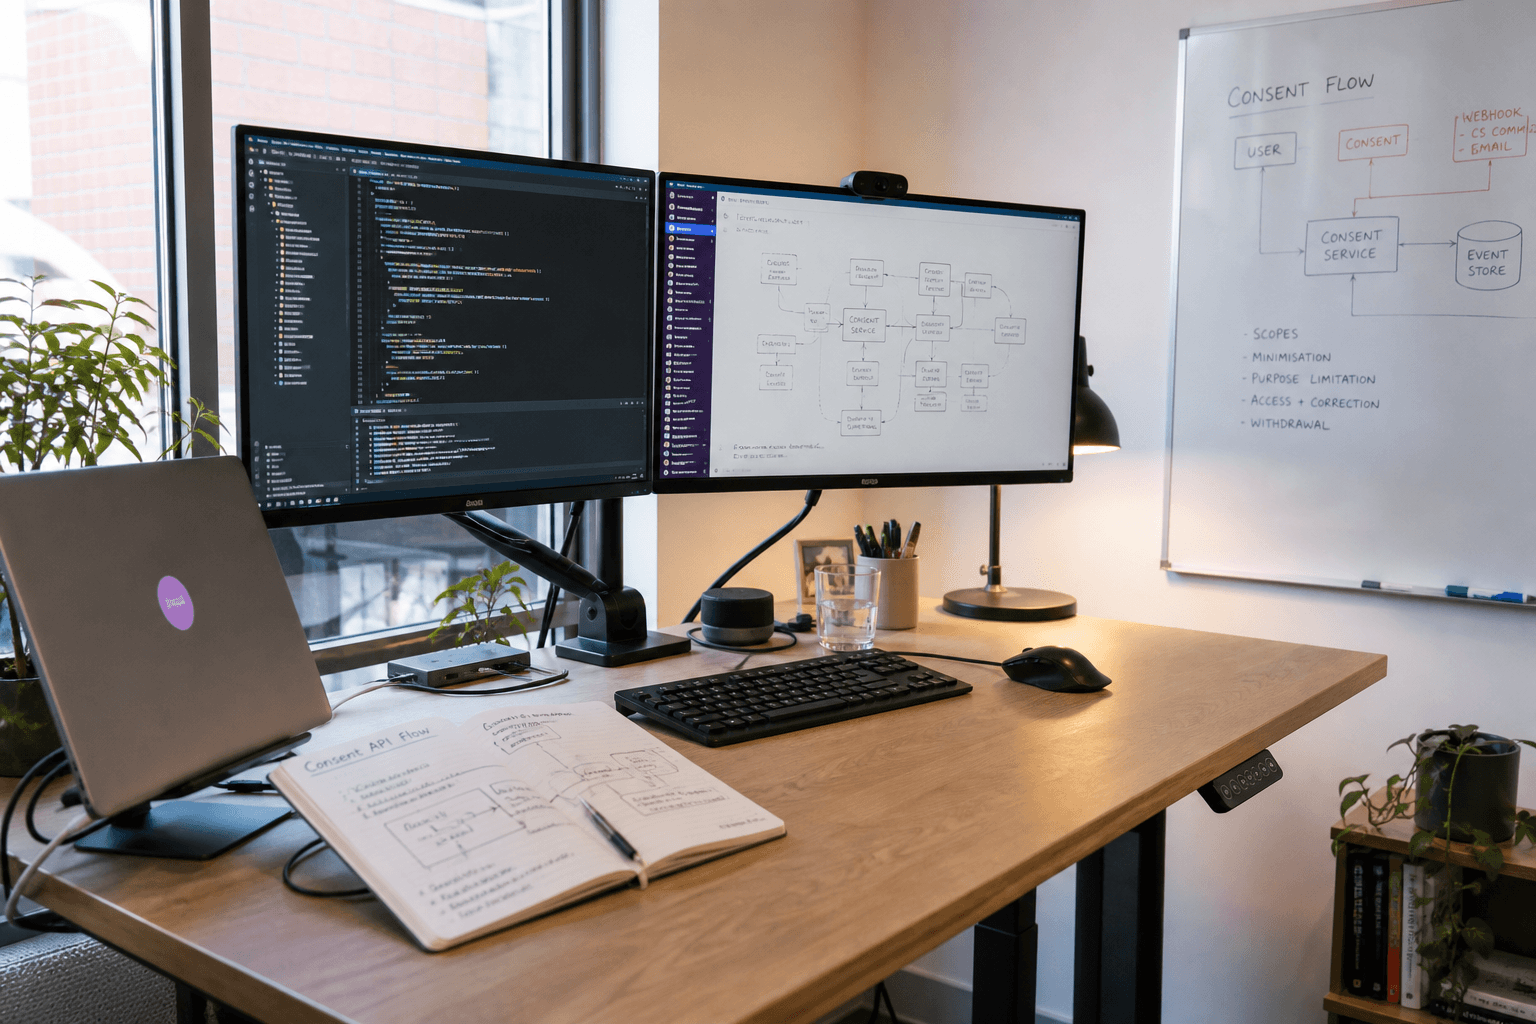
Consent under the CDR is time-bound, purpose-specific, and revocable — and your architecture needs to treat consent as a first-class, auditable data object, not a checkbox stored alongside a user profile. Consent management is the system of record that captures what a consumer agreed to share, for how long, with whom, and for what purpose, and that can prove this history on request from a regulator or the consumer themselves.
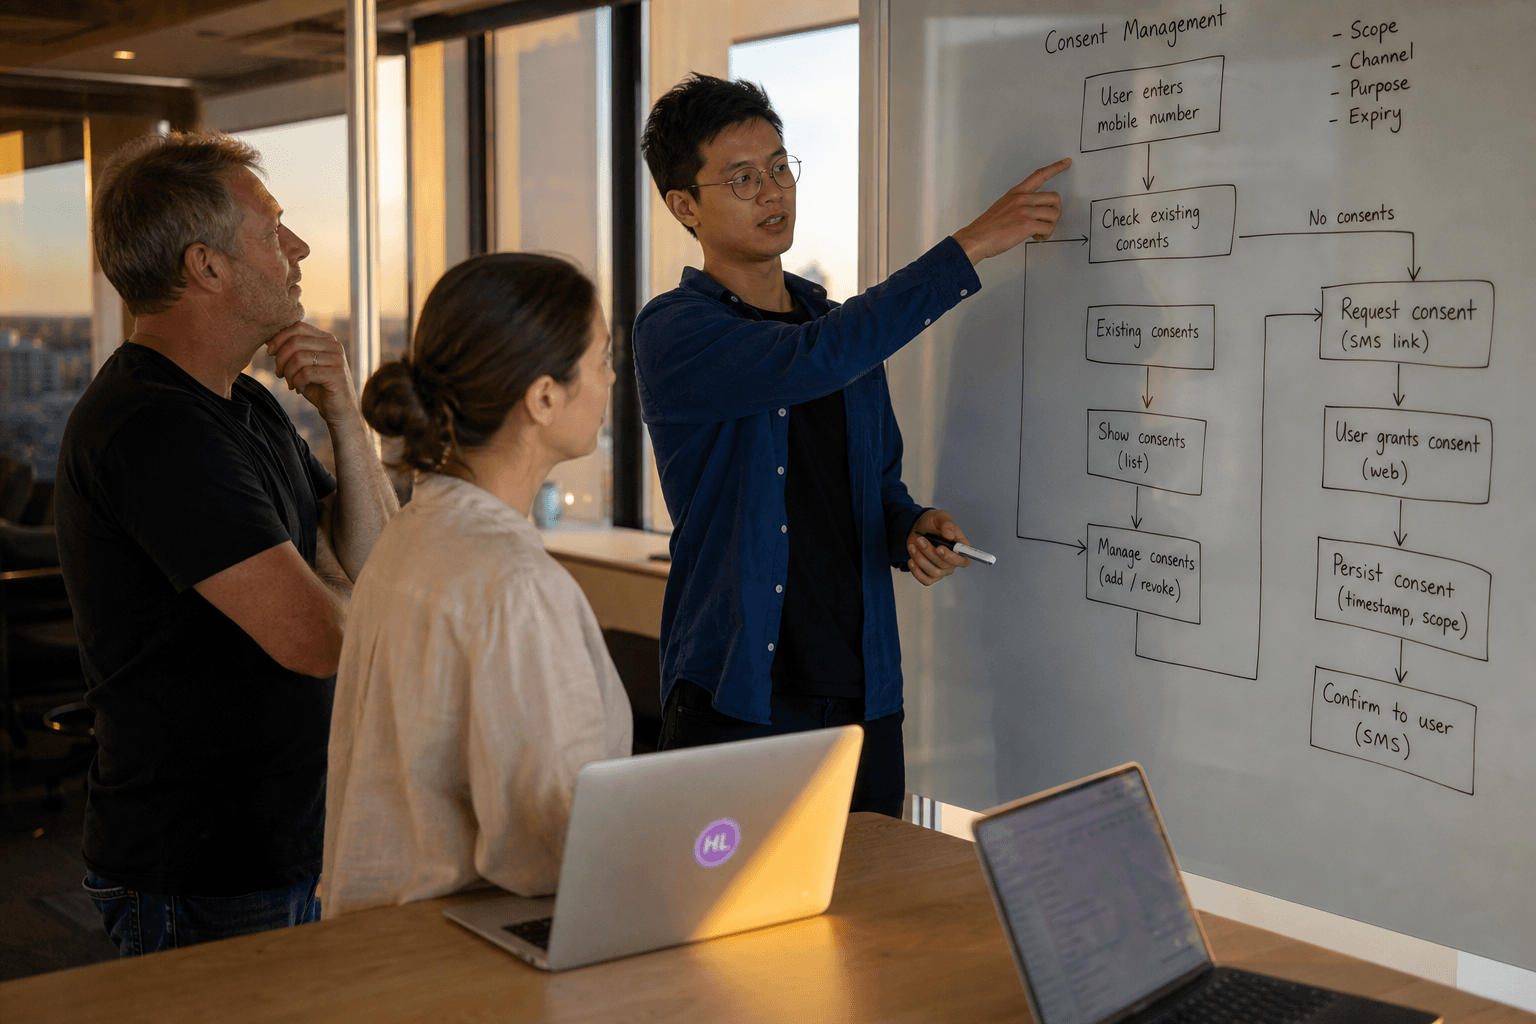
Practically, this means designing a consent ledger that is independent from your core application data model, versioned against the standards' evolving consent-language requirements, and wired into every downstream service that touches CDR-sourced data so access can be revoked in near real time when a consumer withdraws consent. Getting this wrong isn't just a compliance risk — it's an engineering liability, because retrofitting consent enforcement across services that were built assuming permanent access is far more expensive than designing for revocation from the start. A consent event should propagate the same way a security event would: fast, logged, and impossible to silently miss downstream.
This also has implications for anything AI-adjacent built on top of CDR data. If a model has been trained or fine-tuned using data tied to a consent grant that is later revoked, your architecture needs a clear answer for what happens to that model and its outputs — not an assumption that consent revocation only affects live API calls. Teams building analytics or scoring on CDR data should design for this from the outset rather than treating it as a downstream data-governance problem to solve later.
Bringing It Together
None of these three decisions — accreditation pathway, standards-compliant API architecture, and consent-as-a-first-class-object — are independent of each other. The accreditation tier you choose shapes how much of the security profile you own directly. The state of your existing platform shapes how much modernisation work is needed before a clean CDR-compliant API layer is even possible. And the consent architecture you choose determines how safely you can build AI features on top of the data once it's flowing. Teams that treat these as one integrated architecture decision, rather than three separate workstreams, tend to spend less time reworking the integration after launch.
We've written more on the adjacent decisions this raises — including how to decide between building AI capability in-house versus bringing in outside expertise, and how to assess whether your organisation's data foundations are ready for AI adoption — over in more insights.
If your team is scoping a CDR integration, or modernising the platform behind one, we're happy to talk through the architecture decisions before you commit engineering roadmap to them. Get in touch and tell us where you're at.
Chris Kerr
Partner at Horizon Labs, an AI product consultancy and venture studio. A commercially focused product and technology leader with 20+ years building and scaling digital platforms, teams, and businesses across SaaS, travel, eCommerce, logistics and transport, and digital marketing — operating at the intersection of product, engineering, and data. Writes about platform strategy, AI transformation, modern data ecosystems, and the operational discipline that separates AI demos from AI products.